

Apfelpatient
  • Home
  • News
  • Rumors
  • Tips & Tricks
  • Reviews
  • Insights
No result
View All Results
  • iPhone 18
  • iPhone 18 Pro
  • iPhone Duo
  • Apple Home
  • Siri AI
  • HomePod
  • HomePod mini
  • HomePod mini 2
  • MacBook Pro
  • Apple TV 4K
  • Apple Watch Series 12
  • Apple Watch Ultra 4
  • AirPods 5
  • iOS 27
  • iPadOS 27
  • macOS
  • MacBook Neo
  • iPhone 17e
  • AirTags
  • iOS 26
  • iPhone 17
  • iPadOS
  • iMac
  • Mac mini
  • Apple TV
  • iPad Pro
  • iPhone Air
  • Apple Vision Pro
  • iPhone 16
  • AirPods 4
  • Apple Watch Ultra
  • MacBook Air
  • iPad
  • AirPods Max
  • AirPods Pro 3
  • Mac Studio
  • Studio Display
  • iPad Air
  • iPad mini
  • watchOS 27
  • Apple CarPlay
  • Apple Pay
  • watchOS 26
  • Home
  • News
  • Rumors
  • Tips & Tricks
  • Reviews
  • Insights
No result
View All Results
Apfelpatient
No result
View All Results
  • iPhone 18
  • iPhone 18 Pro
  • iPhone Duo
  • Apple Home
  • Siri AI
  • HomePod
  • HomePod mini
  • HomePod mini 2
  • MacBook Pro
  • Apple TV 4K
  • Apple Watch Series 12
  • Apple Watch Ultra 4
  • AirPods 5
  • iOS 27
  • iPadOS 27
  • macOS
  • MacBook Neo
  • iPhone 17e
  • AirTags
  • iOS 26
  • iPhone 17
  • iPadOS
  • iMac
  • Mac mini
  • Apple TV
  • iPad Pro
  • iPhone Air
  • Apple Vision Pro
  • iPhone 16
  • AirPods 4
  • Apple Watch Ultra
  • MacBook Air
  • iPad
  • AirPods Max
  • AirPods Pro 3
  • Mac Studio
  • Studio Display
  • iPad Air
  • iPad mini
  • watchOS 27
  • Apple CarPlay
  • Apple Pay
  • watchOS 26

iOS vulnerability: Apps can read data from other apps

Milan Jovicic by Milan Jovicic
November 12, 2026 - 00:07 CET
in Apple News, iPhone news, rumors and tips
0
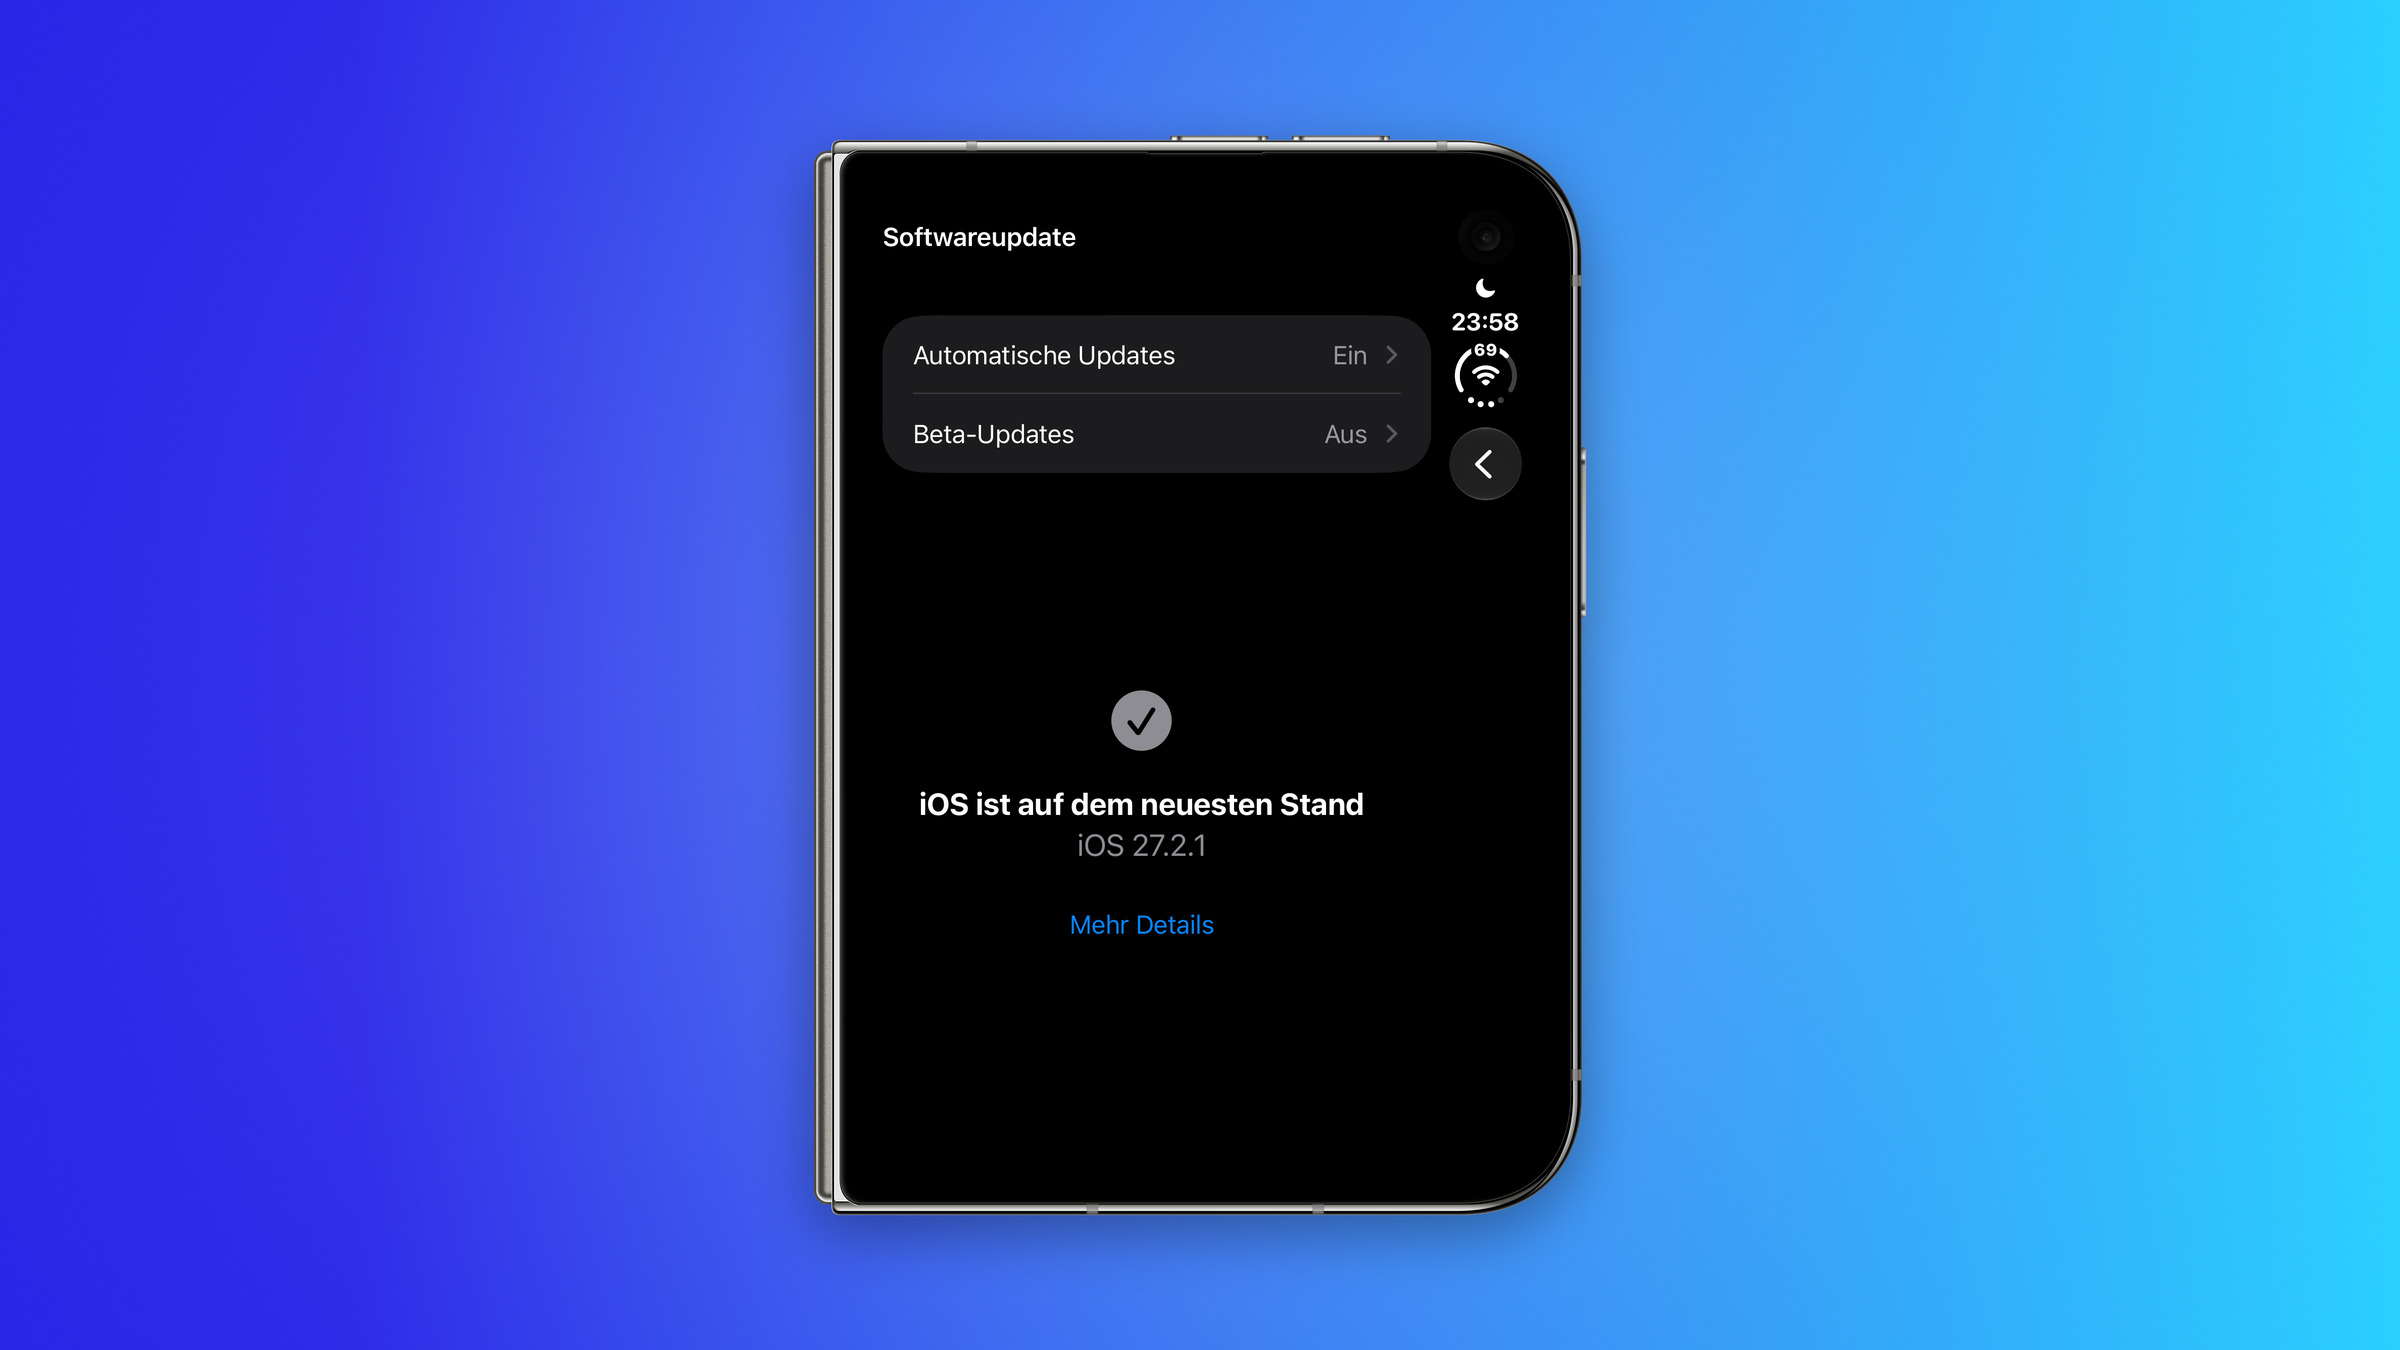
iOS flaw: iPhone Duo showing iOS 27.2.1 as up to date in Software Update

Image: Apfelpatient

WhatsAppFacebookEmail
Threads

This article may contain affiliate links. Learn more on our Partner Program page.

Make Apfelpatient a preferred source One click – and you'll see us more often on Google

A publicly available technique bypasses the separation between apps on the iPhone. The cryptocurrency exchange Binance warns of potential access to seed phrases and private keys. According to the researcher behind the technique, the vulnerability remains unpatched even with the current iOS 27.2.1.

Each app on the iPhone runs in its own sandbox and normally cannot access the data of other apps. This is precisely the boundary that worse_query bypasses. Researchers forcequitOS and 0xjohnny published a proof of concept on GitHub on Sunday, November 8th. Binance issued a warning on Tuesday. In between, iOS 27.2.1 and the other system updates of November 9th were released. Apple's security advisories do not mention a fix specifically attributed to worse_query.

Key Facts at a Glance

  • worse_query is a sandbox escape: A specially crafted app can read files from other apps without jailbreaking.
  • Binance lists iOS 26.7.1, 27.0.1 and 27.2 as affected, while the project page lists iOS 26.0 to 26.7.2 and iOS 27.2.
  • According to forcequitOS, neither iOS 27.2.1 nor iOS 27.3 Beta 1 close the vulnerability.
  • No cases of exploitation or theft have been reported so far.
  • Binance advises deleting apps from unknown sources and updating everything to the latest version.

What Binance specifically fears

The cryptocurrency exchange published its warning on X on November 10th and explicitly did not limit it to its own app:

A vulnerability (worse_query) affecting iOS 26.7.1, 27.0.1, and 27.2 allows malicious apps to read local files from other apps, putting seed phrases, private keys, and login credentials at risk across the entire ecosystem. This is an iOS-level issue, not unique to Binance.

Three recommendations are also available: Delete apps from untrusted sources, such as those installed via sideloading or as manually signed IPA files. Update iOS and all apps to the latest official versions. Anyone who suspects a data breach should transfer their balance to a new wallet on a clean device and reset all active login sessions.

How worse_query bypasses the sandbox

According to the project page, worse_query accesses the data containers of installed apps, the containers of extensions and internal system services, as well as shared app group storage. iOS 27 adds further system paths. A prerequisite is that the app includes its own app group container. The researchers describe the code as a proof of concept for developers, which, on its own, is ineffective, and emphasize that it is not a jailbreak.

How quickly things can change became clear just one day after the release: Developer Christoph Kolbicz introduced WQ Files, a file manager based on worse_query that displays and edits app data under iOS 27 without jailbreaking, tested on iOS 27.0.1. worse_query is the successor to bad_query, which forcequitOS released in the summer for iOS 26.0 to 26.6.1 and the fourth beta of iOS 27.

Whether a wallet actually exposes keys depends on how it stores them. The security company SlowMist sees a particular risk where a wallet stores seed phrases, keystores, or WebView data unencrypted in its own container. Hardware wallets keep the keys away from the phone anyway.

Which versions are affected?

The figures differ because Binance and the researchers cite different numbers:

SourceInformation on iOS versions
Binance warning (November 10th)Affected: iOS 26.7.1, 27.0.1 and 27.2
Project page of worse_queryWorks with: iOS 26.0 to 26.7.2 and iOS 27.2
forcequitOS on X (10.11.)Not closed: iOS 27.2.1 and iOS 27.3 Beta 1

For the current version, forcequitOS has clarified the situation on X:

Just as a general statement so there isn't any confusion about it, worse_query is not patched in iOS 27.2.1 and 27.3 beta 1. I'll update version support on the readme when it's patched.

This also affects the first beta of iOS 27.3, which was released to developers on November 3rd. The head of security at SlowMist had initially stated on the same day that iOS 27.2.1 blocked worse_query; forcequitOS contradicted this with the clarification above.

The security advisories for iOS 27.2.1 do contain an entry regarding app intents, indicating that an app could access sensitive user data. However, this was reported by a different researcher, *worser_query* is not mentioned there, and forcequitOS still considers the vulnerability open. No such entry can be found in the advisories for iOS 26.7.3. There is currently no CVE identifier for *worser_query*.

Why the origin of apps now matters

I consider the situation serious, but not a cause for panic. The attack requires a specially crafted app on the device, and that's precisely where the vulnerability lies. Manually installed enterprise apps only start after they have been explicitly trusted under Settings > General > VPN & Device Management. Checking this section will show whether such apps are present on the device. Anything no longer needed should be uninstalled, as should any other app not from the App Store whose origin is unclear.

In the EU, two additional methods are available: alternative app marketplaces and distribution via websites. Marketplaces have existed since iOS 17.4, and web distribution since iOS 17.5. Anyone who has installed apps from unknown providers via these channels should review the list more critically than usual in the coming days. The other basic rules for protecting against malware on Apple devices remain unchanged.

While the iOS 27.2.1 update doesn't fix the worse_query vulnerability, it's still worthwhile: among other things, it resolves a flaw in iMessage group conversations. Anyone keeping larger sums of money in an iPhone Wallet is better off with a hardware wallet until Apple releases a fix for iOS 27.

Do you have apps from sources other than the App Store on your iPhone, and would you delete them now because of the worse_query warning? Let us know in the comments which sources you use and how you deal with the warning.

Was this article helpful?
YesNo
Tags: iOSiOS 27iOS 27.2.1iPhone
SendShareSend
Share

Our Amazon Storefront

A handpicked selection of products for iPhone, Mac and more – sorted by topic and updated regularly.

Shop Now

This post contains affiliate links (including Amazon). We earn a small commission on qualifying purchases – at no extra cost to you. Learn more on our Partner Program page.

Previous Post

Apple Watch: How to use the new health features

Milan Jovicic

Milan Jovicic

Milan founded Apfelpatient in 2016 and has been responsible for all editorial content since 2018 – news, rumors, how-to guides and product reviews. Here, Apple devices aren't review units kept for two weeks, they're everyday tools: from iPhone to MacBook Pro, MacBook Air and iMac all the way to Apple Vision Pro, at least one device from every product category is in daily use, many of them replaced every year. Every menu path in a guide is checked on the device before it goes live.

Related posts

Apple Support Community: After 28 years, it's over

by Milan Jovicic
November 11, 2026 - 06:06 CET
Apple Support Community: Memoji portraits in colored circles surrounded by app icons such as Photos, Music, iCloud and Home

Apple is closing the Apple Support Community on November 20th. New posts are already blocked; after 28 years, the help forum is ending.

Read moreDetails

MacBook Pro PROLED XDR teardown: 5 out of 10 points

by Milan Jovicic
November 11, 2026 - 00:36 CET
MacBook Pro PROLED XDR Teardown: Two open MacBook Pros in Space Black and Silver, one behind the other, with a background image of light stripes on the displays.

iFixit gives the MacBook Pro with PROLED XDR a score of 5 out of 10. The touchscreen is fine, but the illuminated Apple logo is a problem.

Read moreDetails

iPhone supplier Tata: Three workers die in India

by Milan Jovicic
November 11, 2026 - 00:06 CET
iPhone supplier Tata: Unfolded iPhone Duo in landscape on a grey surface, its display showing Apple Maps with the city of Hosur.

Three temporary workers have died at the Tata Electronics factory in Hosur, which manufactures iPhone components. Authorities are reviewing safety regulations.

Read moreDetails

AirPods: Apple rolls out new firmware 9B47

by Milan Jovicic
November 10, 2026 - 11:24 PM CET
AirPods firmware 9B47: White AirPods Max 2 with case seen from above on a grey surface, with the iPhone Duo in a blue Folio above them.

New AirPods firmware 9B47 for AirPods Pro 2, Pro 3, AirPods 4, 5 and Max 2: Which version was valid before and how to check for the update.

Read moreDetails

Apple TV: New Fraggles special starts on December 4th

by Milan Jovicic
November 10, 2026 - 7:25 PM CET
Fraggles special on Apple TV: Key art for "Fraggle Rock: A Holiday Gift" with five Fraggles gathered around a glowing snow globe in a wintry cave.

Apple TV is showing the trailer for „Fraggle Rock: A Big Gift“. The holiday special starts on December 4th, also with a German dub.

Read moreDetails
Load More

Leave a Reply Cancel reply

Required fields are marked with * marked.

By submitting, you consent to the storage of your comment along with your name, email address and IP address. Details are available in our privacy policy.

Categories

  • Apple Insights
  • Apple Rumors
  • Apple News
  • Apple Tips & Tricks
  • iPhone news, rumors and tips
  • Mac and MacBook News
  • Reviews
Make Apfelpatient a preferred source One click – and you'll see us more often on Google

About APFELPATIENT

APFELPATIENT brings you the latest Apple news, product updates, guides, reviews and tips across the entire Apple ecosystem — from the iPhone to the Mac to the Apple Vision Pro. From the first rumors to confirmed news: researched responsibly.

Follow Apfelpatient

Facebook Instagram YouTube Threads Threads

Company

  • About Apfelpatient
  • Contact
  • Author Profiles

Community

  • Netiquette
  • Push notifications
  • RSS feed

Legal

  • Legal Notice
  • Privacy Policy
  • Terms of Use
  • Cookie settings
  • Affiliate Program

Resources

  • Sitemap

© 2026 Apfelpatient. All rights reserved.

No result
View All Results
  • Home
  • News
  • Rumors
  • Tips & Tricks
  • Reviews
  • Insights

© 2026 Apfelpatient. All rights reserved. Site map

Change language to Deutsch


