apple patient
  • Home
  • News
  • Rumors
  • Tips & Tricks
  • Reviews
  • Insights
No Result
View All Result
  • iPhone 18
  • iPhone 18 Pro
  • iPhone Duo
  • Apple Watch Series 12
  • Apple Watch Ultra 4
  • AirPods 5
  • iOS 27
  • iPadOS 27
  • macOS
  • MacBook Neo
  • iPhone 17e
  • AirTags
  • iOS 26
  • iPhone 17
  • MacBook Pro
  • iPadOS
  • iMac
  • Mac mini
  • HomePod
  • Apple TV
  • iPad Pro
  • iPhone Air
  • Apple Vision Pro
  • iPhone 16
  • AirPods 4
  • Apple Watch Ultra
  • HomePod Mini
  • MacBook Air
  • iPad
  • AirPods Max
  • AirPods Pro 3
  • Apple Watch Series 3
  • Mac Studio
  • Studio Display
  • iPad Air
  • iPad mini
  • watchOS 27
  • Apple CarPlay
  • Apple Pay
  • watchOS 26
  • Home
  • News
  • Rumors
  • Tips & Tricks
  • Reviews
  • Insights
No Result
View All Result
apple patient
No Result
View All Result
  • iPhone 18
  • iPhone 18 Pro
  • iPhone Duo
  • Apple Watch Series 12
  • Apple Watch Ultra 4
  • AirPods 5
  • iOS 27
  • iPadOS 27
  • macOS
  • MacBook Neo
  • iPhone 17e
  • AirTags
  • iOS 26
  • iPhone 17
  • MacBook Pro
  • iPadOS
  • iMac
  • Mac mini
  • HomePod
  • Apple TV
  • iPad Pro
  • iPhone Air
  • Apple Vision Pro
  • iPhone 16
  • AirPods 4
  • Apple Watch Ultra
  • HomePod Mini
  • MacBook Air
  • iPad
  • AirPods Max
  • AirPods Pro 3
  • Apple Watch Series 3
  • Mac Studio
  • Studio Display
  • iPad Air
  • iPad mini
  • watchOS 27
  • Apple CarPlay
  • Apple Pay
  • watchOS 26

FileVault: New vulnerability discovered in Intel chips

Milan Jovicic by Milan Jovicic
March 6, 2020 - 17:32 CET
in Apple News
0
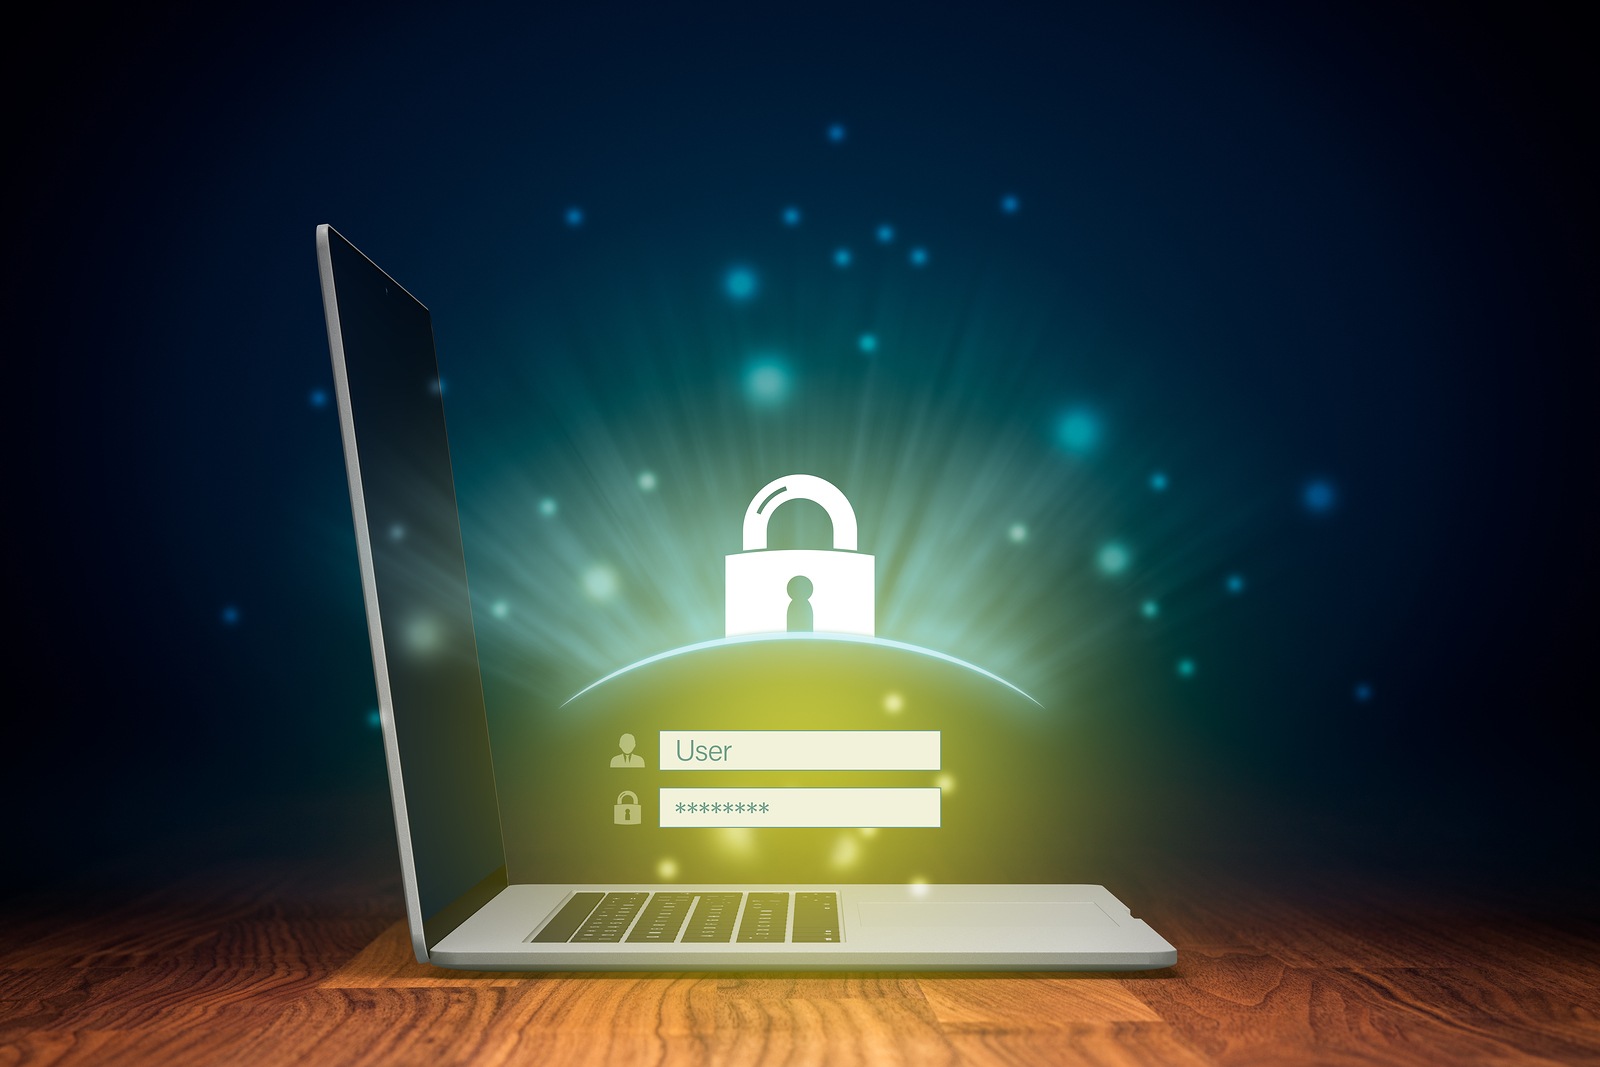
Cybersecurity and computer security concept. Notebook and login screen and padlock symbolizing computer security.

Cybersecurity and computer security concept. Notebook and login screen and padlock symbolizing computer security.

WhatsAppFacebookEmail
Threads

Following the Meltdown and Spectre security vulnerabilities, a new hardware-based exploit has now been discovered in Intel chips. This is said to make Apple's FileVault technology vulnerable. 

Last year, the Meltdown and Spectre security vulnerabilities were discovered, which caused a lot of trouble. According to current reports, the security vulnerabilities at that time have since been fixed. But now there seems to be a new problem and it is said to be unpatchable. According to reports, the SSD encryption FileVault on Mac devices without T1 and T2 chips is at risk. 

The purpose of FileVault

FileVault technology is essentially designed to encrypt the entire hard drive. It uses the AES128-bit XTS standard encryption by default. However, Disk Utility also offers the AES256-bit XTS version, a military-grade encryption that makes Macs 100 percent secure. However, according to a new report from The Register, this very "feature" is at risk. A brand-new hardware-based vulnerability in Intel chips could make FileVault vulnerable, as the security hole is said to be unpatchable. According to initial findings, attackers could compromise the Mac's boot process to gain access to the code responsible for encrypting the hard drive. The problem is described as follows: explained: 

The problem revolves around cryptographic keys that, if obtained, can be used to break the root of trust in a system. Buried deep inside modern Intel chipsets is what is known as the Management Engine, or nowadays the Converged Security and Manageability Engine (CSME).

Like a digital janitor, the CSME works behind the scenes, beneath the operating system, hypervisor, and firmware, performing many important low-level tasks such as booting up the computer, controlling power levels, starting the main processor chips, verifying and booting the motherboard's firmware, and providing cryptographic functions. The engine is the first thing that runs when a machine is turned on. One of the first things it does is set up memory protections on its own built-in RAM so that other hardware and software cannot interfere with it. However, these protections are disabled by default, so there is a tiny time gap between when a system is turned on and the CSME executing the code in its boot ROM that installs these protections, which come in the form of input-output memory management unit (IOMMU) data structures called page tables.

During this time gap, other hardware - physically connected or present on the motherboard - capable of firing a DMA transfer into the CSME's private RAM can overwrite variables and pointers and take over execution. At this point, the CSME can be seized for malicious purposes without the software running on top of it noticing. It's like a sniper shooting a sliver of a target while shooting past small cracks in a wall. The DMA write race can be attempted when the machine is powered on or awakens from sleep. If someone manages to extract this hardware key, they can unlock the chipset key and, with code execution within the CSME, undo Intel's root of trust in large product areas at once. When this happens, total chaos will reign. Hardware IDs will be spoofed, digital content will be extracted, and data from encrypted hard drives will be decrypted.

Therefore, the Mac should not be released

The exploit is not only hardware-based, but also considered unpatchable. Anyone who passes their Mac on to third parties makes themselves vulnerable, as the vulnerability can only be exploited if attackers gain physical access to the device. Intel's advice is that the affected devices must remain in the "physical possession" of the owner. However, not all Macs are affected. According to the report, Apple devices with the T1 and T2 security chips are not affected, as these are activated before the Intel chip when the Mac boots up, and the FileVault encryption keys are stored in the "Secure Enclave." Therefore, only "older" devices are affected by the problem. (Photo by Jakub Jirsak / Bigstockphoto)
  • Kr00k: Security flaw discovered in Wi-Fi encryption
Make Apfelpatient a preferred source One click – and you'll see us more often on Google
Was this article helpful?
YesNo
Via: The Register
Tags: Macsecurity gap
SendShare37Send
Share

Our Amazon Storefront

A handpicked selection of products for iPhone, Mac and more – sorted by topic and updated regularly.

Shop Now

This post contains affiliate links (including Amazon). We earn a small commission on qualifying purchases – at no extra cost to you. Learn more on our Partner Program page.

Previous Post

Backup: WhatsApp tests new security feature

Next Post

Apple recommends employees work from home

Milan Jovicic

Milan Jovicic

Milan founded Apfelpatient in 2016 and has been responsible for all editorial content since 2018 — news, rumors, guides, and product reviews. Apple devices here are not test units on loan for two weeks but everyday tools: from the iPhone through MacBook Pro, MacBook Air, and iMac to the Apple Vision Pro, at least one device from nearly every product category is in daily use, many of them replaced annually. Every menu path in a guide is verified on the device before it is published.

Related posts

watchOS 27.2: Code reveals new screenshot preview

by Milan Jovicic
September 24, 2026 - 8:36 p.m. CEST
Apple Watch Ultra with an orange band showing the app view, the device getting the new screenshot preview in watchOS 27.2

watchOS 27.2 includes a new screenshot interface for the Apple Watch: preview, share, and delete, just like on the iPhone. It's currently inactive.

Read moreDetails

Apple TV: Peanuts classics free again for Christmas

by Milan Jovicic
September 24, 2026 - 6:43 p.m. CEST
Charlie Brown holding a small Christmas tree under a starry sky in the snow, a scene from A Charlie Brown Christmas, free again on Apple TV

Three classic Peanuts cartoons are back on Apple TV for the holidays, no subscription required. Plus, there are new specials featuring Snoopy and the Fraggle Rocks.

Read moreDetails

The Wanted Man: Hugh Laurie on Apple TV from January

by Milan Jovicic
September 24, 2026 - 6:19 p.m. CEST
Hugh Laurie as crime boss Felix Carmichael in an evening scene from The Wanted Man on Apple TV

The Wanted Man premieres on January 6, 2027 on Apple TV. Hugh Laurie plays a crime boss who wants to escape – the finale is in February.

Read moreDetails

Apple and Qualcomm extend patent license from 2027

by Milan Jovicic
September 24, 2026 - 6:04 p.m. CEST
Back of an iPhone 18 Pro Max in a burgundy case on a grey surface, covered by the renewed Apple Qualcomm patent license

Apple and Qualcomm are extending their patent license from April 2027. Why this has nothing to do with the modem change and affects Germany.

Read moreDetails

iPhone 18 Pro: Update to prevent Face ID restarts is coming

by Milan Jovicic
September 24, 2026 - 1:13 p.m. CEST
iPhone showing the General settings with Software Update, where the fix for the Face ID reboots on iPhone 18 Pro will arrive

Apple has confirmed an update to fix the restarts after failed Face ID recognition on the iPhone 18 Pro and Pro Max. An exchange is not worthwhile.

Read moreDetails
Load More

Categories

  • Apple Insights
  • Apple Rumors
  • Apple News
  • Apple Tips & Tricks
  • iPhone news, rumors and tips
  • Mac and MacBook News
  • Reviews

About APFELPATIENT

APFELPATIENT brings you the latest Apple news, product updates, guides, reviews and tips across the entire Apple ecosystem — from the iPhone to the Mac to the Apple Vision Pro. From the first rumors to confirmed news: researched responsibly.

Follow Apfelpatient

Facebook Instagram YouTube Threads Threads

Company

  • About Apfelpatient
  • Contact
  • Author Profiles

Community

  • Netiquette
  • Push Notifications
  • RSS feed

Legal

  • Legal Notice
  • Privacy Policy
  • Terms of Use
  • Cookie Settings
  • Affiliate Program

Resources

  • Sitemap

© 2026 Apfelpatient. All rights reserved.

No Result
View All Result
  • Home
  • News
  • Rumors
  • Tips & Tricks
  • Reviews
  • Insights

© 2026 Apfelpatient. All rights reserved. Page Directory

Change language to Deutsch